
Last updated: 2026-11-06
c5-readiness.de is run by Blackfort Technology UG (haftungsbeschränkt), Ernst-Robert-Curtius-Straße 8A, 53117 Bonn, Germany. The company has been registered in the commercial register of the Bonn Local Court (Amtsgericht Bonn) since 2017 (HRB 23120) and is owner-managed. We work in information security, compliance and technical implementation: with us, regulatory classification and implementation in the systems come from the same project. The founder and managing director is Christian Gebhardt.
What C5-Readiness is
C5-Readiness brings together our services around the BSI C5 criteria catalogue. It is aimed at cloud and SaaS providers that need a C5 attestation, often because a customer or a tender requires one and a deadline is fixed. We focus in particular on providers of AI software in healthcare and on providers that already hold an ISO 27001 certificate or a SOC 2 report and want to build on it.
On this website we explain the C5:2026 catalogue, the audit and the preparation. The service behind it is C5 consulting up to audit readiness, starting with the C5 readiness assessment.
Founder and managing director: Christian Gebhardt
Christian Gebhardt, Managing Director since 2017
| Period | Role | Company |
|---|---|---|
| 2021-2024 | Deputy CISO | Gothaer Solutions GmbH |
| 2020-2021 | Information Security Officer | Gothaer Solutions GmbH |
| 2021-2023 | Managing Director | ArcSin GmbH |
| 2017-2019 | Audit Specialist | Deutsche Bank Group |
| 2015-2016 | Security Consultant | TÜV Trust IT |
| 2014-2015 | IT Security Consultant | exceet Secure Solutions |
| 2007-2014 | Working student, IT Solution Architect, Junior Systems Engineer | BWI Informationstechnik |
- Permanent member of the AI Expert Working Group
Alliance for Cyber Security / BSI - Co-author: “Guidelines for Penetration Testing of Large Language Models” (ACS/BSI)
Christian Gebhardt founded Blackfort Technology in 2017, alongside his role as an audit specialist at Deutsche Bank.
The professional background he brought with him continues to shape how Blackfort works today. He started as a working student at BWI Informationstechnik, the IT service provider of the German Federal Armed Forces, and stayed for seven years. From 2011 he worked there as an IT Solution Architect and systems engineer, responsible for directory services, identity and access management and the BWI PKI based on the PKI of the German Armed Forces. This was followed by roles at exceet Secure Solutions in the Gematik telehealth infrastructure with a focus on PKI and Hardware Security Modules, and at TÜV Trust IT, where he led ISO 27001 ISMS build-out projects at municipal critical infrastructure organisations.
Deutsche Bank opened the perspective of independent review: audit leadership in highly regulated domains - BAIT, MaRisk, ZAG, KRITIS - covering topics such as information security management, payment processing, PKI and data centre security. This experience at times revealed just how far apart documented requirements and lived practice can be.
After his role as Information Security Officer at Gothaer Solutions GmbH, he became Deputy CISO in 2021, leading the information security team with a direct reporting line to the IT board member.
In parallel, from 2021 to 2023 he served as Managing Director of ArcSin GmbH, a company specialising in artificial intelligence and cryptography with a focus on massively parallel processing in distributed systems - an early engagement with AI architecture well before the topic became mainstream for security organisations.
In the field of AI security, he is a permanent member of the AI Expert Working Group of the Alliance for Cyber Security (ACS/BSI). He co-authored the ACS “Guidelines for Penetration Testing of Large Language Models” (2025) and wrote its first draft.
This work has nothing to do with C5 or with audits under C5.
Why we do not issue attestations
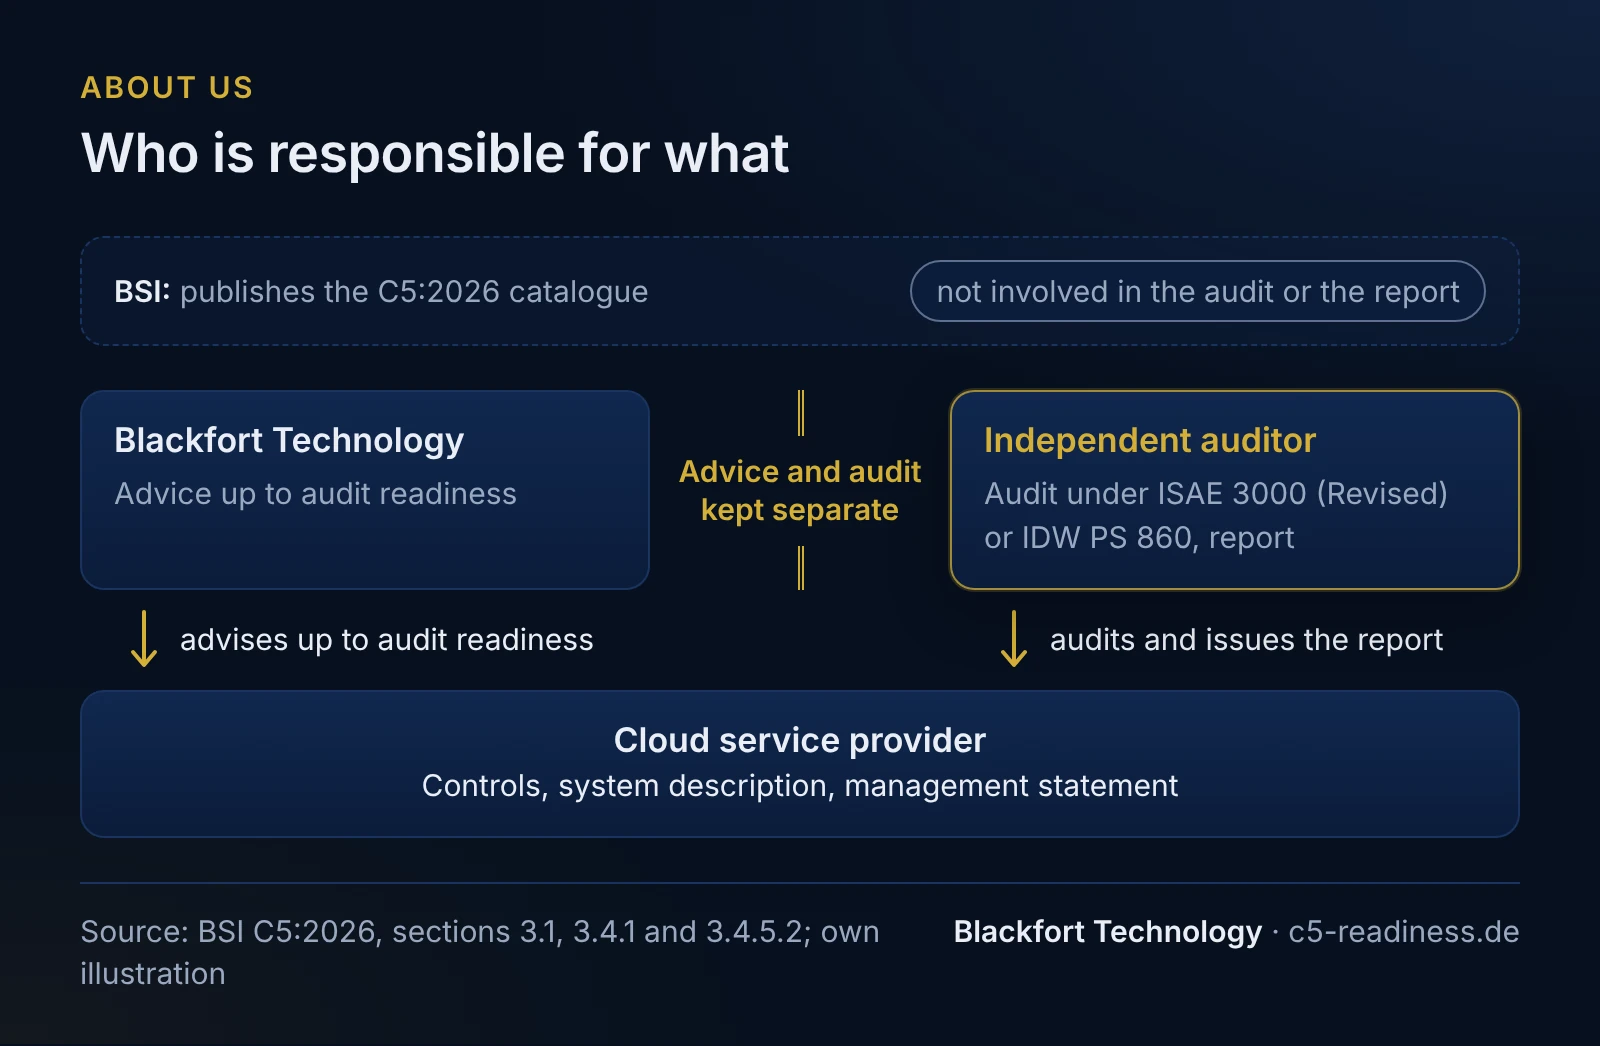
Whoever helped build a system should not audit it. That is why we keep advice and audit strictly apart: Blackfort Technology prepares, an independent auditor audits and issues the report. We use our audit experience to prepare you for the auditor’s questions, not to audit you ourselves.
The catalogue requires a reasonable assurance engagement under ISAE 3000 (Revised) or a national equivalent such as IDW PS 860 (section 3.4.1). Before accepting an engagement, the auditor has to determine that its professional duties, including independence, are complied with, in Germany under Section 43 of the Public Accountant Act (Wirtschaftsprüferordnung, WPO) (section 3.4.2). The BSI itself is not involved in the audit or the report (section 3.1).
This gives us three rules for our work:
- We do not issue attestations or certificates. According to the BSI, there is no such thing as a C5 certificate anyway, only attestations.
- We have no partnership with an audit firm. You choose and engage the auditor. We help you make proposals comparable.
- Your management issues the management statement on its own basis. We prepare the documents, but we do not sign anything on your behalf.
How we work
Our approach has five steps, which also fit a C5 project:
- Understand the service, components and dependencies: which service, which components, which service providers and platforms.
- Identify risks: where the controls do not yet meet the criteria and what that means for the deadline and the report type.
- Derive measures: a prioritised plan with owners and sequence.
- Implement technically: together with your teams we implement configuration, processes and documentation.
- Evidence and audit readiness: file evidence so that it can be demonstrated across the audit period, and complete the system description.
Your enquiry is received by Christian Gebhardt as founder and managing director. Who works on the project is set out in the proposal. We work in German or English, by video conference and on site where the project needs it.
Example: how working together begins
Fictitious example, not a client. A hosting provider that runs Kubernetes clusters for software companies gets in touch because a tender from a public contracting authority requires a C5 attestation. In the initial call we clarify the service, the deadline and the existing documents. We then propose a C5 readiness assessment with a fixed scope. Its result is an action plan with project planning, on the basis of which the provider decides for itself whether and how to continue working with us.
Why we do not name clients
We do not name clients or projects on this website, because confidentiality is part of consulting. Instead of references we show our method, a fictitious sample result of the C5 readiness assessment and freely usable templates.
Blackfort Technology is a partner of Tenable, Rapid7 and DigiCert. These partnerships concern security tools and certificate services. They have nothing to do with the C5 audit.
What you can expect from us
- We back statements about the catalogue with the reference in the C5:2026 catalogue and the date of the information.
- We say what the catalogue requires, what our recommendation is and what is an example, and keep these visibly apart.
- We do not promise an attestation or a deadline that we cannot influence. The report is issued by the auditor.
- On Section 393 SGB V and other legal provisions we provide general information. The legal assessment of your case belongs with a lawyer.
Frequently asked questions
Does Blackfort Technology issue C5 attestations?+
Do you work with a particular audit firm?+
Does Blackfort Technology act on behalf of the BSI?+
Where is Blackfort Technology based?+
Read more
Sources
- Blackfort Technology: company website (retrieved 2026-11-01)
- Blackfort Technology: Über uns (career of Christian Gebhardt, German) (retrieved 2026-11-06)
- Blackfort Technology: About us (career of Christian Gebhardt) (retrieved 2026-11-06)
- Imprint of c5-readiness.de (German) (retrieved 2026-11-01)
- Imprint of c5-readiness.de (retrieved 2026-11-06)
- BSI: Kriterienkatalog Cloud Computing C5:2026, version 1.1.0 (PDF, German), sections 3.1, 3.4.1, 3.4.2 and 3.4.5.2, licensed under CC BY-ND 4.0 (retrieved 2026-11-01)
- BSI: C5 FAQ (German; no certification scheme, no C5 certificates) (retrieved 2026-11-01)
This content provides general technical and organisational information and does not constitute legal advice (no legal services within the meaning of the German RDG).