
Last updated: 2026-11-01
The C5 check is a first assessment of where you stand, for cloud and SaaS providers preparing evidence under the BSI C5 catalogue. In a few minutes it shows which questions you should settle first and which pages help with them. An assessment of each individual criterion only comes with the C5 readiness assessment.
Start the self-check
Eight short steps, about five minutes. The evaluation runs in your browser and appears straight away; your answers are neither stored nor transmitted. They only leave your browser if you explicitly send the result to us at the end.
Our cookieless analytics (Matomo) only records that the check was started and the result was shown, and whether you then clicked the contact link, without your answers. Please do not enter any personal data or health data; the check does not ask for them either.
What the check asks
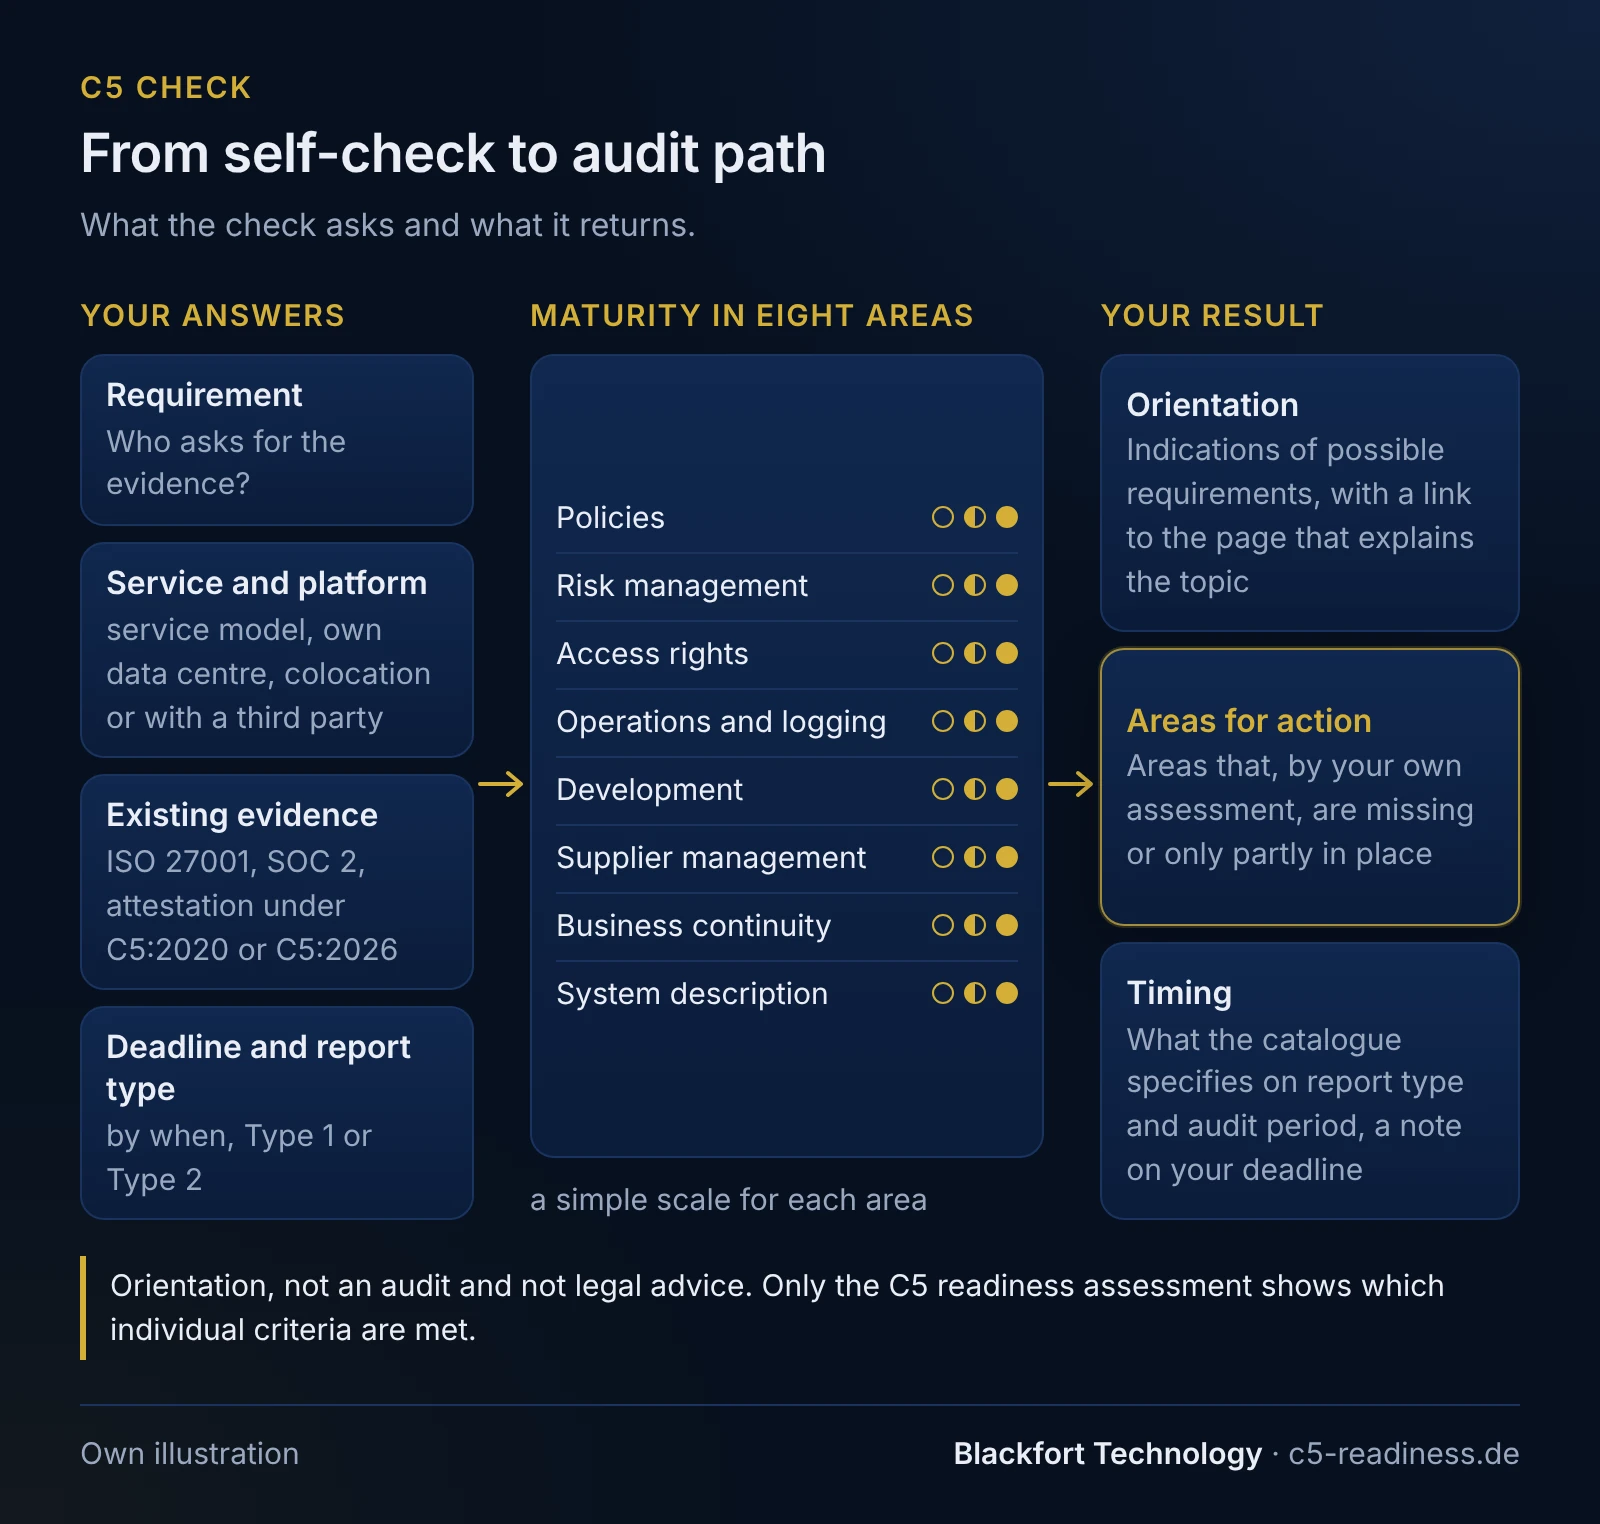
- Requirement: whether an enterprise customer, a tender, customers in the healthcare sector, a federal authority or the financial sector expects the evidence.
- Service and platform: the service model and whether the service runs in your own data centre, on your own hardware in rented space (colocation) or with a third party. This determines how the scope is drawn.
- Existing evidence: an ISO 27001 certificate, a SOC 2 report or a C5 attestation under C5:2020 or C5:2026.
- Deadline and report type: by when a report should be available and whether you are aiming for type 1 or type 2.
- Maturity in eight areas: policies, risk management, access rights, operations and logging, development, supplier management, business continuity and the system description, each on a simple scale.
How to read the result
The result has three parts. The orientation names indications of possible requirements that follow from your answers and links to the page that explains the topic. The areas for action rank the areas that, by your own assessment, are missing or only partly in place. The timing part sums up what the catalogue specifies on report type and audit period and gives a note on how well your deadline fits. For detailed planning, work back from the deadline as described on the page on the C5 audit process.
Limits of the self-check
The check rests only on your own assessment and on a few simplified questions. It gives indications of possible requirements, but it makes no legal statement on whether a provision such as Section 393 SGB V applies to your service. The legal assessment of the individual case is a matter for your legal advisers. Whether an attestation is issued is decided by the auditor alone. Blackfort Technology does not audit and does not issue attestations.
The check does not ask for any personal data or health data, and you do not upload any audit reports or documents.
Frequently asked questions
Are my answers stored?+
Does the check tell me whether I need a C5 attestation?+
How accurate is the assessment of the areas for action?+
Read more
- C5 readiness assessment: gap analysis, action plan and timeline
- BSI C5 audit process: steps, audit standards and timeline
- C5 type 2 or type 1 report: differences, period, choice
- C5 scope: service boundary, platform reports, carve-out
- Section 393 SGB V: C5 attestation for healthcare cloud services
- Free C5 templates: scope sheet, evidence register, CUEC matrix
Sources
- BSI: Kriterienkatalog Cloud Computing C5:2026, version 1.1.0 (PDF, German), licensed under CC BY-ND 4.0 (retrieved 2026-11-01)
- BSI: C5 FAQ (German) (retrieved 2026-11-01)
- Section 393 SGB V (Book V of the German Social Code; German) (retrieved 2026-11-01)
- C5 Equivalence Ordinance (C5GleichwV, German) (retrieved 2026-11-01)
This content provides general technical and organisational information and does not constitute legal advice (no legal services within the meaning of the German RDG).