
Last updated: 2026-11-01
This page helps you draw up a budget your management can approve: with clearly separated items, the factors that determine the effort, and a list of the information without which no quote is comparable. How the audit itself runs is covered on the C5 audit process page.
What makes up the cost of a C5 attestation?
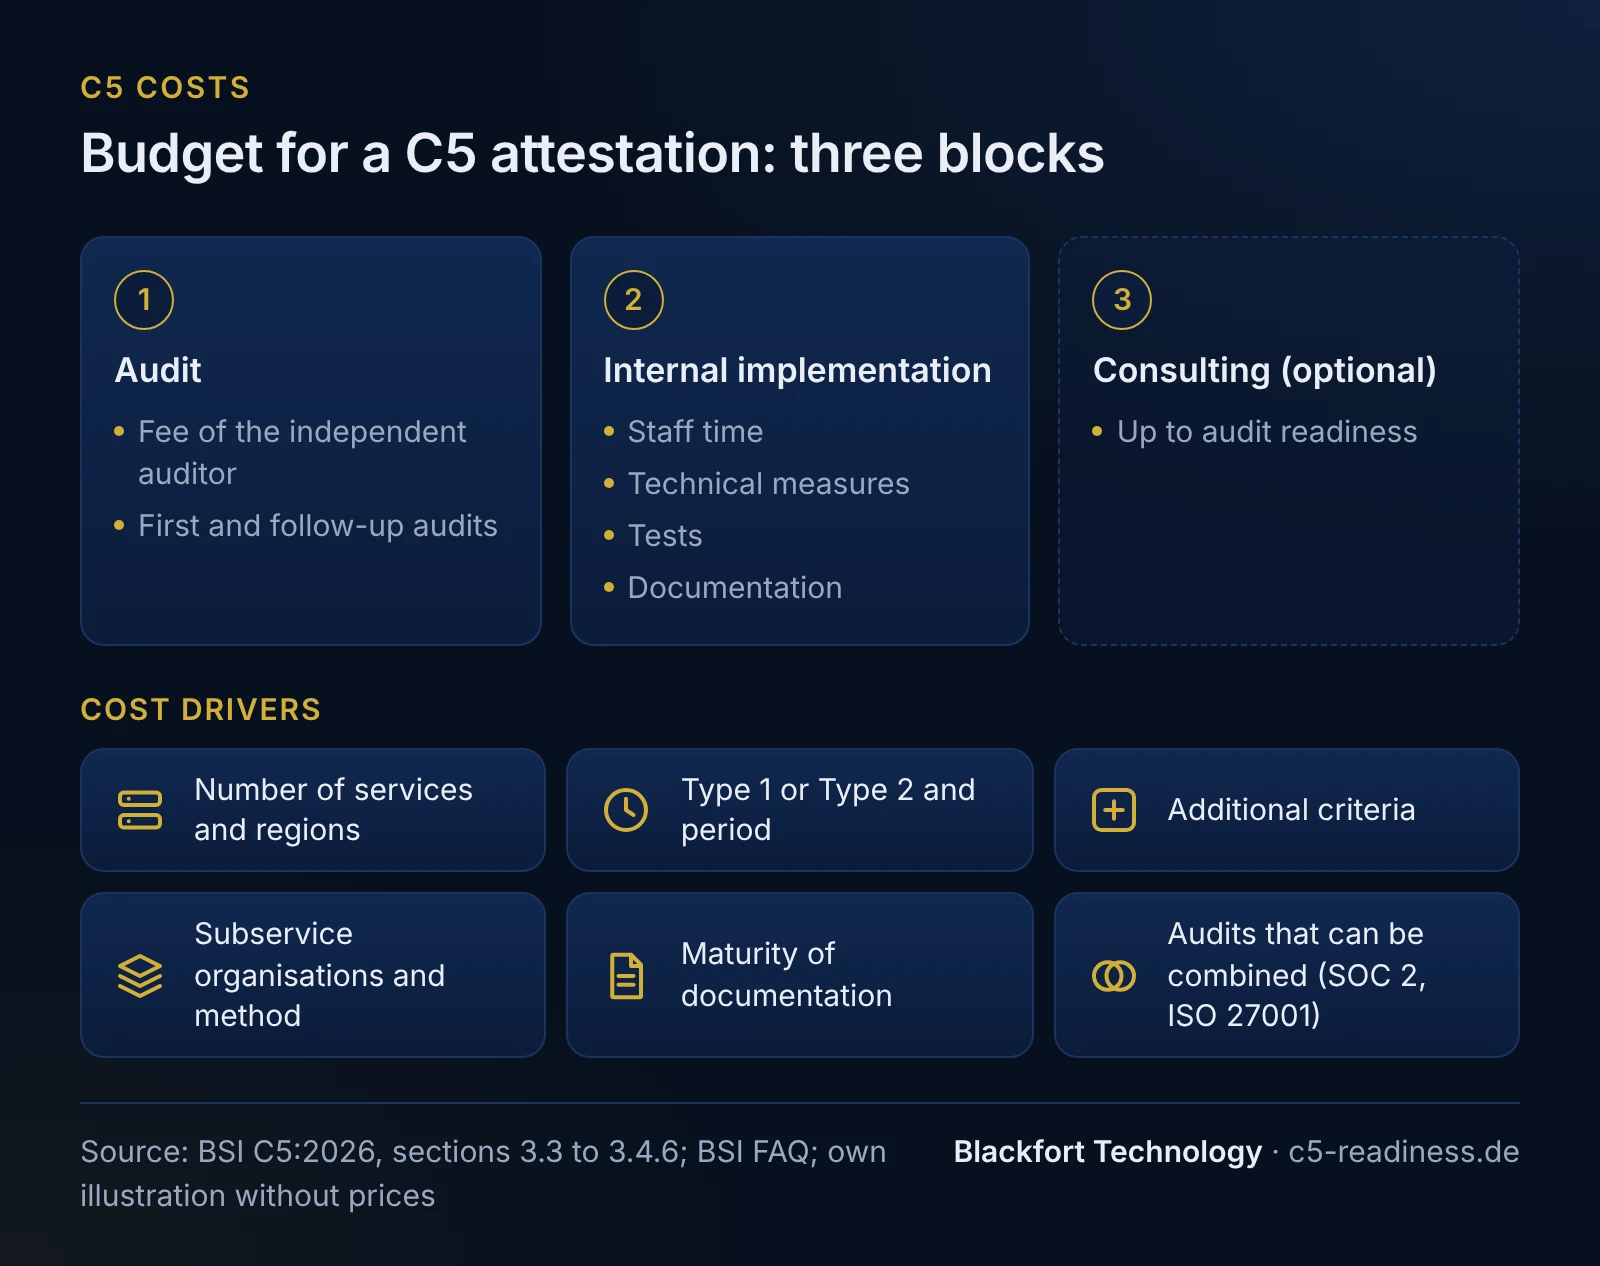
Three blocks, which you should plan separately because they come from different sources and grow in different ways.
| Block | What it includes | Who provides the figure | One-off or recurring |
|---|---|---|---|
| Audit | Fee of the independent auditor for planning, audit procedures and report; first audit and follow-up audits | Quotes from auditors based on your scope | recurring, as audits are usually repeated every year |
| Internal implementation | Working time of your teams, technical measures and tools, tests, training, documentation, support during the audit | Your own planning, based on a gap analysis | one-off build-up, then operation |
| Consulting (optional) | Gap analysis, action plan, system description, preparation for the audit | Quotes from consultants | mainly before the first audit |
There is a factual reason for the separation: whoever advises does not audit. Before accepting the engagement, the auditor has to ensure its independence (catalogue, section 3.4.2). Blackfort Technology supports you up to audit readiness; the attestation is issued by an independent auditor whom you engage separately.
What does the auditor charge for the audit?
We do not give a figure for this. On 1 November 2026 we searched for public information on fees for C5 audits. All we found were ranges on third-party websites, without report type, scope, services included and whether VAT is included, or without a traceable origin. Such a range would suggest more certainty than it can provide, so we do not publish it.
What is established: the auditor is usually engaged and paid by the cloud service provider (catalogue, section 3.1; BSI FAQ). For a reliable figure, obtain two to three quotes based on the same written scope. Only then are the quotes comparable.
What drives audit costs?
The audit effort grows with what has to be audited. The main drivers can be derived directly from the catalogue:
| Driver | Why it has an effect | Catalogue or source |
|---|---|---|
| Number of services and regions | The attestation applies only to the audited services in the specified regions; each additional service extends the subject matter of the audit. | BSI FAQ; system description, minimum content item 1 |
| Type 1 or type 2, length of the period | Type 2 also tests operating effectiveness over a period which, according to the catalogue, should usually cover three to twelve months; for this the auditor needs evidence from the entire period. | Sections 3.4.4 and 3.4.11 |
| Additional criteria | The basic criteria are the minimum scope; each additional criterion included is added to it. | Section 3.4.3 |
| Subservice organisations and method | Under the inclusive method the auditor also tests controls at the subservice organisation; under carve-out they remain outside the audit. | Sections 1.2.2 and 3.4.6 |
| Maturity of documentation | If there is no system description, a direct engagement may be considered, in which the auditor documents the system itself. | Sections 3.4.4 and 3.4.13 |
| Combination with other audits | SOC 2, ISAE 3402 or ISO audits can be aligned with the C5 audit in timing and organisation; the BSI cites cost and time savings from a joint audit. | Section 3.3; BSI FAQ |
| Move to C5:2026 | Adjusted controls count as significant changes; depending on the period, the description needs information on planned changes. | Section 3.5 |
An existing ISO 27001 certificate does not automatically reduce the effort: results from ISO certification audits have to be assessed differently from those of an ISAE 3000 engagement (section 3.3). What can be reused is shown on the C5 and ISO 27001 page, and for SOC 2 on the C5 and SOC 2 page.
Is type 1 cheaper than type 2?
For the individual audit, the scope of type 1 is smaller, because operating effectiveness over a period is not tested. For planning over several years, however, this is what counts: type 1 is only permitted for the first engagement, and every follow-up audit is type 2 (section 3.4.4). If you start with type 1, you pay for two audits before a type 2 report exists. A type 1 report is not a prerequisite for type 2 (section 3.4.11). Whether the interim step is worthwhile depends on whether your customers accept a type 1 report; see type 1 or type 2.
What does internal implementation cost?
This is the block only you can put a figure on, because it depends on the distance between where you are today and the criteria. Plan for at least these items:
- Working time: information security, operations, development, HR, procurement and management, for the build-up, evidence and supporting the audit.
- Technical measures: for example logging and evaluation of events (OPS-13), vulnerability management, hardening, key management.
- Tests required by the catalogue: for example penetration tests (OPS-22) and tests of business continuity planning (BCM-04).
- Training and awareness for employees (HR-03).
- Managing service providers: evaluating the reports of platform and other subservice organisations (SSO-05), see C5 scope.
- Documentation: policies, control descriptions, evidence register and the system description.
- Ongoing operation: controls have to keep running after the attestation; every follow-up audit is type 2.
Our recommendation: do not run this block as a staff estimate alone. The gap analysis should give you one action per gap with an owner and a rough effort estimate, otherwise the budget remains a guess.
What does consulting cost?
Consulting is optional and does not replace either of the other two blocks. It makes sense where there is no internal experience with ISAE 3000 audits: in defining the scope, in the gap analysis, the action plan and the system description. Compare consulting quotes by scope of services and result, for example whether you end up with a prioritised action plan and a description that is ready for audit. How to start with Blackfort Technology is described on the C5 readiness assessment page.
What information do auditors and consultants need for a quote?
The more complete this list, the more comparable the quotes. We recommend sending it to all providers as a short scope sheet:
- Service or services with service model (SaaS, PaaS, IaaS) and functionality
- Regions and locations of processing
- Desired report type and specified date or period, catalogue version
- Type of engagement: attestation engagement or direct engagement
- Desired additional criteria and the reason for them
- Subservice organisations with their role, existing C5 reports and desired method
- Existing certificates and reports (ISO 27001, SOC 2, ISAE 3402) with scope and period
- State of documentation: policies, control descriptions, existing system description
- Size of the organisation and number of teams performing controls
- Customer deadline by which the report must be available
- Language of the report
- Planned follow-up audits and desired frequency
The scope sheet is available as a template on the templates page.
Example: budget framework for a SaaS provider
Fictitious example, without prices. A provider of practice management software as SaaS with 40 employees, an ISO 27001 certificate for the company and operations on an IaaS platform in Germany plans a first audit as type 2.
| Item | Driver in the example | Basis for the figure |
|---|---|---|
| Audit, first audit | one service, one region, basic criteria only, a six-month type 2 period, platform under carve-out | three auditor quotes based on the same scope sheet |
| Audit, following years | annual type 2 audit with a subsequent period | ask for the follow-up price in the same quote |
| Internal implementation | ISMS in place, gaps mainly in service-specific controls, management of service providers and evidence | action plan from the gap analysis with effort per action |
| Penetration test | one test before the period begins | quote from a testing provider |
| Consulting | gap analysis, system description, audit preparation | consulting quote with a fixed scope of services |
| Contingency reserve | rework after gaps reported by the auditor | management’s own allowance |
The table does not replace a calculation. It shows which figure comes from whom, so that nothing is budgeted twice or not at all.
Frequently asked questions
What does a C5 attestation cost?+
Who pays for the C5 audit?+
Are the costs one-off?+
Does an existing SOC 2 report save costs?+
Can a consultant make the attestation cheaper?+
Read more
- BSI C5 audit process: steps, audit standards and timeline
- C5 scope: service boundary, platform reports, carve-out
- C5 type 2 or type 1 report: differences, period, choice
- C5 vs ISO 27001: what you can reuse and what is missing
- C5 vs SOC 2: reusing your SOC 2 report for a BSI C5 attestation
- Choosing a C5 auditor: qualifications and IDW PS 860
- C5 readiness assessment: gap analysis, action plan and timeline
Sources
- BSI: Kriterienkatalog Cloud Computing C5:2026, version 1.1.0 (PDF, German), sections 3.1 to 3.5, licensed under CC BY-ND 4.0 (retrieved 2026-11-01)
- BSI: Cloud Computing Compliance Criteria Catalogue C5:2026, version 1.0.1 (PDF), sections 3.1 to 3.5, licensed under CC BY-ND 4.0 (retrieved 2026-11-06)
- BSI: C5 FAQ (German) (retrieved 2026-11-01)
This content provides general technical and organisational information and does not constitute legal advice (no legal services within the meaning of the German RDG).